
PHP Attack Threatens Crypto Safety: Should You Cash Out or Pull Funds From Exchanges?

The FBI, National Security Agency (NSA), and Cybersecurity and Infrastructure Security Agency (CISA) have warned organizations to urgently patch two important PHP assault dubbed “PHP2Shell,” which may let hackers take management of weak servers with out logging in. With PHP powering web sites and net functions worldwide, the warning raises a urgent query for crypto security: Should you money out Bitcoin or pull funds from exchanges to guard your crypto?
The PHP2Shell vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619, may permit attackers to execute malicious code on weak servers with out authentication. Both flaws carry a important CVSS v4.0 rating of 9.2, prompting cybersecurity businesses to induce organizations to patch affected programs instantly.
The PHP assault creates a possible danger for crypto exchanges, pockets suppliers, and decentralized finance (DeFi) platforms that depend upon weak net infrastructure. But it doesn’t robotically compromise Bitcoin, Ethereum, or non-public keys saved securely offline.
Could Hackers Reach Your Crypto in This PHP Attack?
PHP powers web sites and functions, together with companies that will deal with account data, authentication, and monetary transactions. The newly disclosed vulnerabilities may let attackers execute code on affected servers, probably exposing delicate data or permitting additional compromise.
The PHP Foundation launched fixes on October 21, 2026, together with PHP 8.5.12, 8.4.27, 8.3.36, and eight.2.35. Administrators working affected programs ought to set up the suitable updates, whereas organizations utilizing managed internet hosting ought to verify that their suppliers have addressed the vulnerabilities.

Cloudflare has additionally reported assault site visitors concentrating on clients and deployed net software firewall protections. Those defenses will help block malicious requests, however they don’t exchange patching weak software program.
For us, crypto holders, the bottom line is between an infrastructure vulnerability and a confirmed breach. A compromised alternate backend may create dangers for buyer data or account safety, relying on what the attacker can entry. Yet the existence of the PHP assault alone doesn’t set up that any explicit alternate has been breached.
Discover: Crypto IPO to Watch This Q4
Should You Withdraw From Exchanges or Cash Out?
The reply is direct, not solely due to PHP2Shell. There is at the moment no foundation for treating each alternate account or self-custody pockets as compromised just because these vulnerabilities exist.
Withdrawing funds from an alternate could cut back publicity to sure exchange-specific dangers, however it additionally introduces different concerns, together with withdrawal charges, community errors, phishing scams, and the safety of the vacation spot pockets. Moving crypto to a different platform with out checking its safety may merely alternate one danger for an additional.
Selling crypto is a special determination. A PHP assault is a cybersecurity occasion, not direct proof that Bitcoin or Ethereum costs should fall. Cashing out primarily based on a headline may depart buyers reacting to a menace that by no means impacts their very own holdings.
For higher Crypto security, we must always first decide if the alternate or pockets supplier has issued a related warning, if their account reveals suspicious exercise, and whether or not their credentials or restoration phrase may have been uncovered.
If a supplier confirms a breach affecting buyer belongings, comply with its official directions and assess the precise publicity earlier than deciding whether or not to withdraw or switch funds.
Ledger Attack Raises Separate Hardware Wallet Concerns
The PHP assault arrives amid separate considerations about {hardware} pockets safety.
In an October 12 report, we lined Ledger’s investigation right into a {hardware} implant present in a minimum of one system related to the CryptoBilis reseller. The investigation linked affected units to reported wallet-draining incidents, with estimates reaching $93 million throughout 311 wallets on 5 blockchain networks. The complete stays an estimate relatively than a confirmed ultimate loss determine.
The Ledger incident is separate from PHP2Shell. It highlights a special crypto security concern: {hardware} supply-chain tampering relatively than a vulnerability in server software program. Neither incident establishes that every one Ledger units are compromised.
Hardware wallets will help defend non-public keys, however Crypto security nonetheless relies on how units are sourced, how restoration phrases are saved, and whether or not customers confirm transaction particulars earlier than signing.
Read the complete report: What Ex Mt.Gox CEO Found, and How to Protect Your Crypto
PHP Attack Crypto Safety Checklist: What We Should Do Now?
We can take a number of sensible steps with out making rushed monetary selections. First, replace pockets functions and units by official channels. Second, overview current transactions and token approvals for unfamiliar exercise. Third, by no means enter a restoration phrase into a web site or share it with somebody claiming to offer technical assist.
Hardware pockets homeowners ought to comply with their producer’s official steerage, notably in the event that they bought units by a reseller related to a safety investigation. Anyone who has credible proof {that a} restoration phrase was uncovered ought to create a brand new pockets with a brand new seed phrase on a trusted system and switch remaining belongings securely.
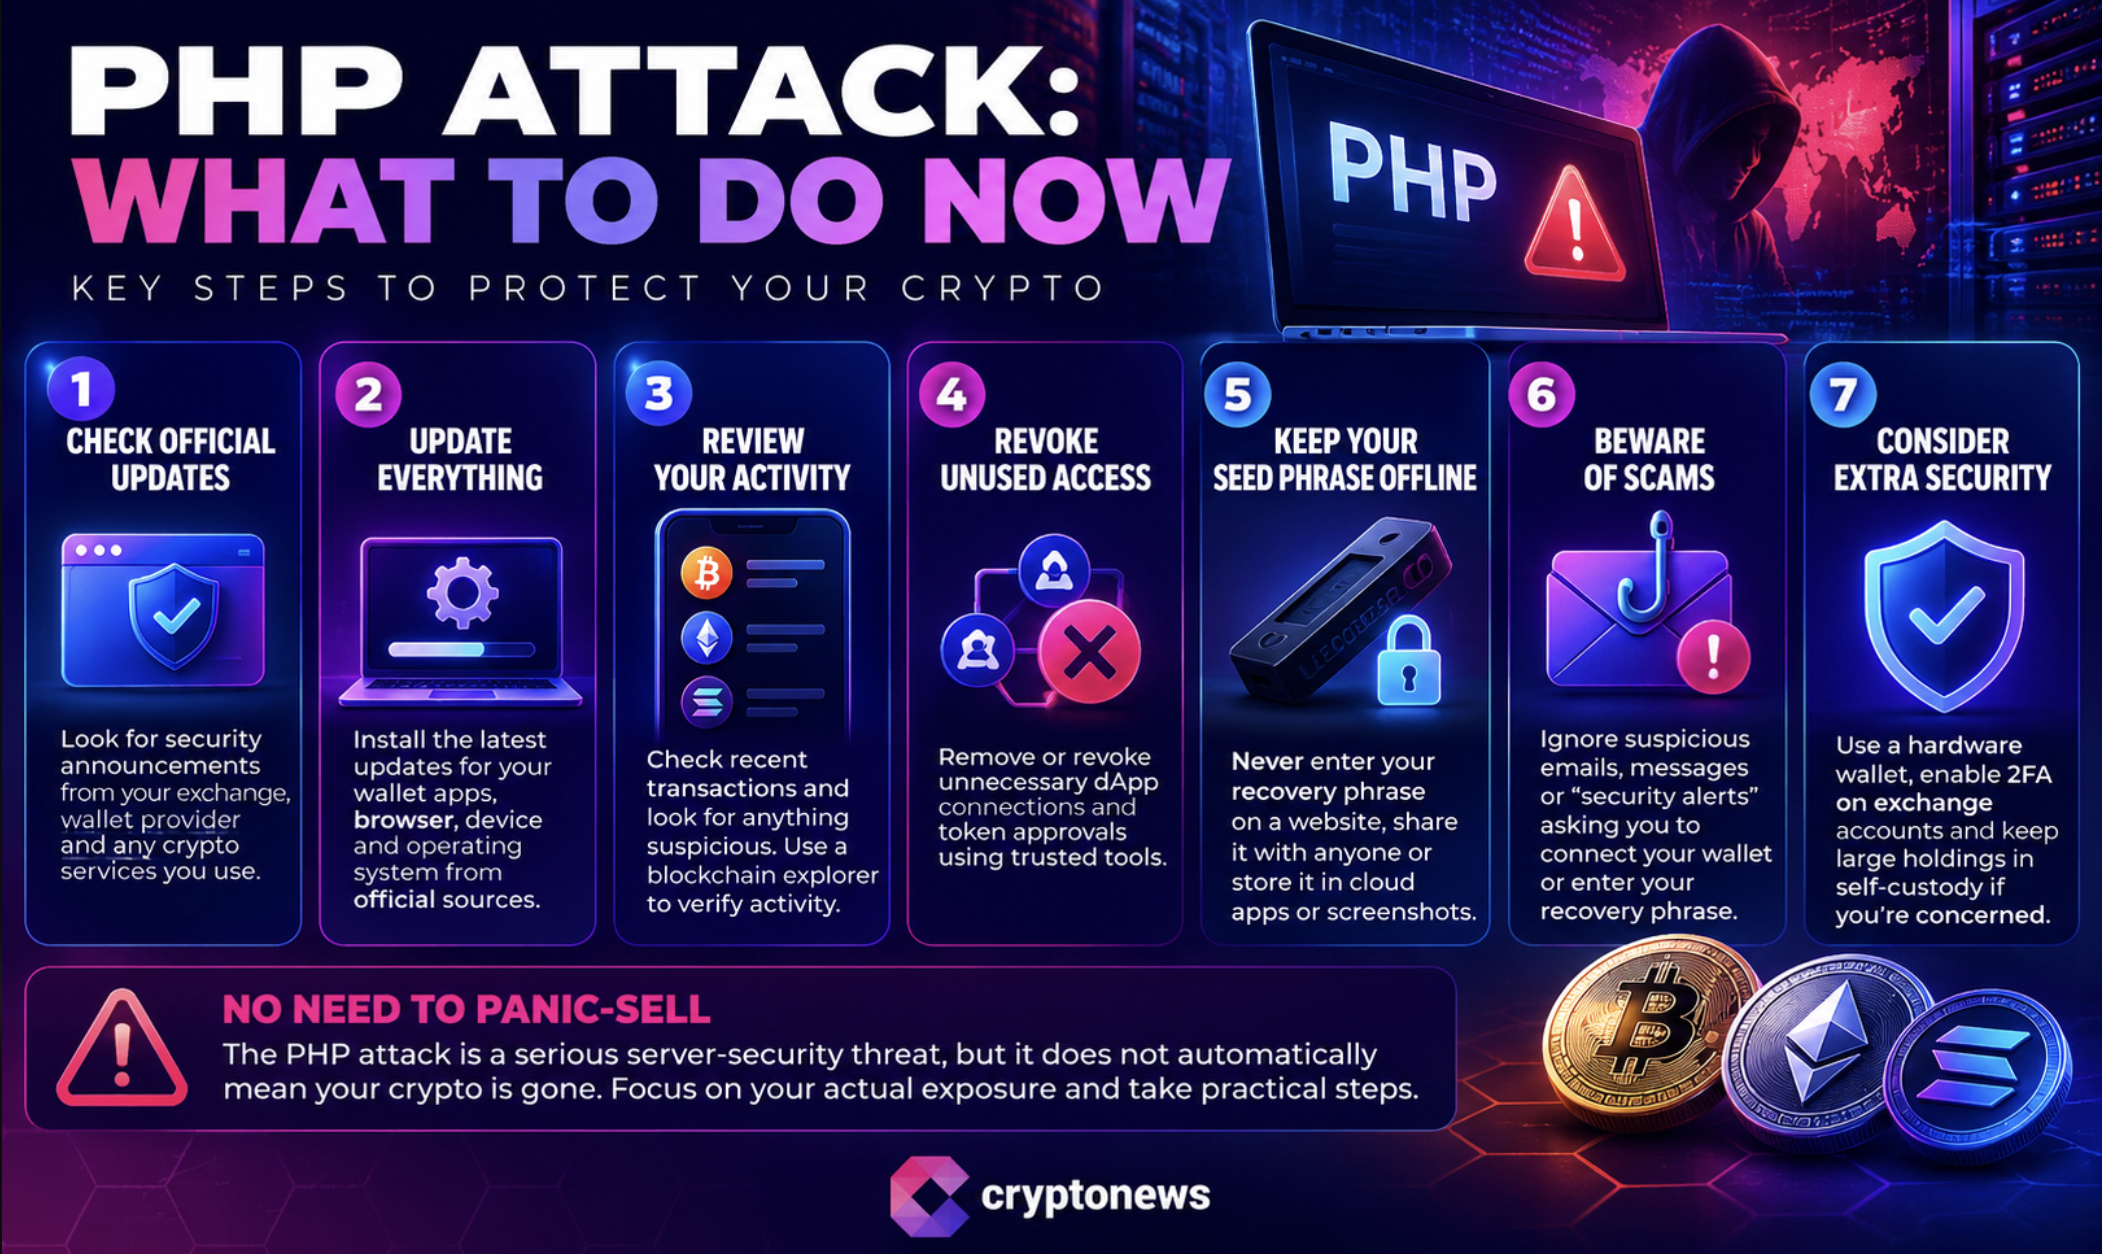
Finally, monitor official bulletins from exchanges, pockets producers, and related safety businesses. Organizations working weak PHP servers must patch urgently; abnormal buyers ought to concentrate on their very own publicity relatively than treating each vulnerability as an instruction to promote.
PHP2Shell is a severe server-security menace, however it’s not an automated crypto pockets drain. For now, we don’t must money out or withdraw funds solely due to the PHP assault. Checking suppliers, securing credentials, and responding to confirmed publicity supply a extra focused strategy to Crypto security.
Discover: The Best Token Presales
The submit PHP Attack Threatens Crypto Safety: Should You Cash Out or Pull Funds From Exchanges? appeared first on Cryptonews.