
Two Safe Wallets Lose $305,000 in FlashLoopAdapter Attack

A customized FlashLoopAdapter used to handle leveraged Aave V3 positions was exploited in a hack on Ethereum, leaving two Safe wallets with an estimated internet lack of 114.09 ETH, or about $305,000.
The attacker spoofed a Safe authentication examine, then used a Morpho WETH flash mortgage to repay debt and unlock collateral. The roughly 1,306 weETH withdrawn from one pockets was a gross transaction circulation, not the attacker’s internet proceeds.
Defimon Alerts mentioned it detected the Ethereum assault at 15:08:57 UTC on Thursday, October 1. SlowMist printed its evaluation on Friday, October 2, figuring out a weak spot in the adapter’s open and shut features. A malicious contract might pose as a Safe and return that worth, passing a examine supposed to verify {that a} reliable pockets had enabled FlashLoopAdapter.
The AAVE hack attacker-controlled contract additionally provided the adapter’s swap router and calldata. It pointed the router at a sufferer Safe and set the calldata to invoke execTransactionFromModule. Because FlashLoopAdapter was already enabled on that Safe, the pockets accepted the decision as a certified module transaction.
The sequence turned a slim authentication flaw into entry to wallet-controlled collateral. The episode underscores how pockets permissions and execution paths matter alongside the safety of the lending protocol itself, a priority additionally central to custody infrastructure and authentication controls.
Earn $50 and Enter $300K Prize Draw on EdgeX
Flash Loan Hack Repaid Aave Debt Before Collateral Was Withdrawn
The attacker used a Morpho flash mortgage denominated in WETH to repay roughly 1,335 WETH of Aave debt related to the bigger Safe. Repayment freed collateral tied to its leveraged place, permitting roughly 1,306 weETH to be withdrawn. A second Safe misplaced about 6.4 weETH via the identical weak module.
Both affected Safes had the identical single proprietor. After the borrowed funds have been settled and a few belongings transformed, the attacker retained roughly 114.09 ETH, which safety experiences valued at about $305,000.
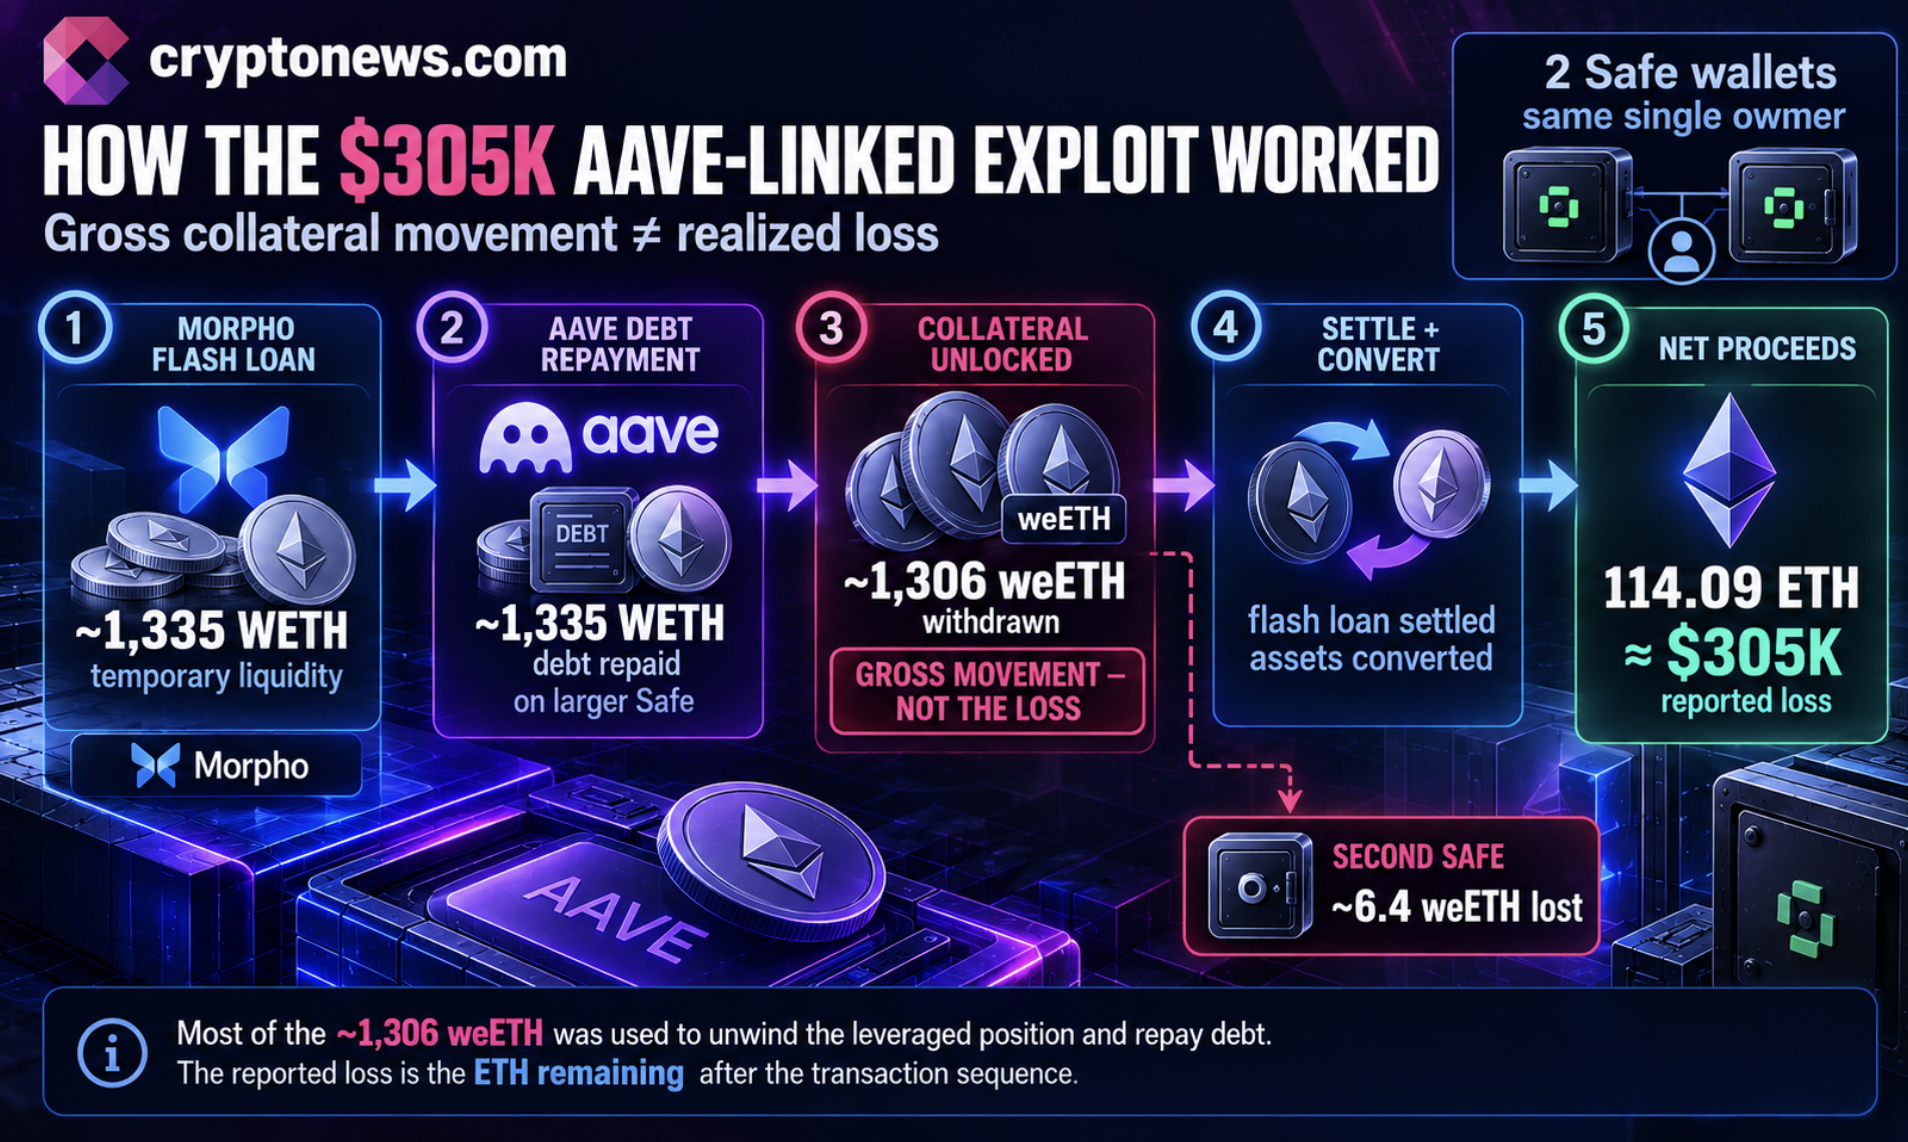
The distinction between gross motion and realized loss is materials. The giant collateral withdrawal enabled the debt reimbursement and place unwind; it shouldn’t be learn as the quantity stolen. The reported internet proceeds have been the ETH remaining after these transaction steps.
Trade AAVE on Bybit and Get a Chance to Win Our $1,000 USDT Airdrop
Aave Says Core Contracts Not Affected
Aave founder and CEO Stani Kulechov mentioned the weak element was an exterior integration quite than an Aave V3 contract and had “zero impact on Aave v3.”
SlowMist labeled the incident as a smart-contract vulnerability and attributed the bypass to the spoofable Safe examine. Defimon described FlashLoopAdapter as a Safe module for opening and shutting leveraged Aave V3 loops and estimated the loss at roughly $305,000.
FlashLoopAdapter is a customized contract constructed on Aave V3 for managing leveraged positions in Safes that enabled it. Safe modules can execute pockets transactions with out requiring the usual proprietor transaction circulation every time, which helps automation but additionally offers a certified module a path to pockets belongings.
Here, the module’s permission was not itself the reported bug; the adapter’s caller-authentication and execution logic have been. The case is subsequently a DeFi safety failure on the integration layer, not proof that Aave V3’s lending swimming pools have been compromised.
The main supply additionally notes a separate September Safe-wallet incident involving roughly 2,900 rsETH and weak authorization in an executor linked to an enabled module, however the two incidents concerned distinct contracts and assault paths.
Discover: The Best Token Presales
The publish Two Safe Wallets Lose $305,000 in FlashLoopAdapter Attack appeared first on Cryptonews.


